
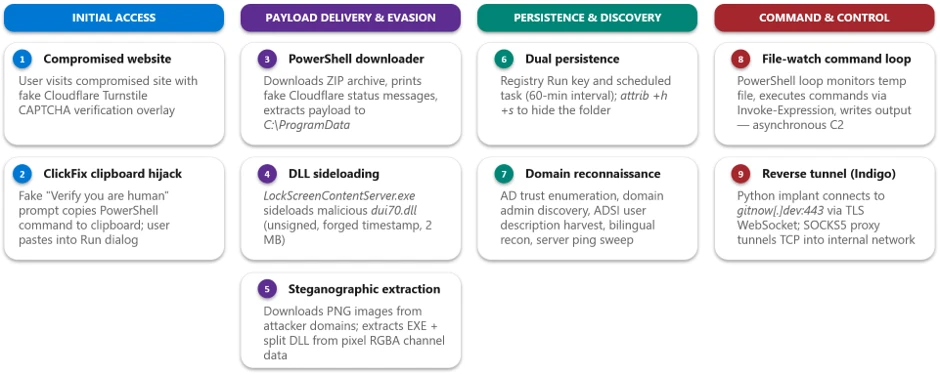
Bottom line: Attackers are using a multistage intrusion technique involving a reverse tunnel to evade detection by traditional security controls.
What's happening: The ClickFix campaign, attributed to the APT41 group, uses fake CAPTCHA prompts to trick users into installing a malicious DLL, which in turn establishes a reverse tunnel through the compromised endpoint's network traffic.
What to do: Security leaders should monitor for suspicious DLL activity and implement additional controls to prevent DLL sideloading, including configuring Windows Firewall to block incoming connections to known malicious domains.