
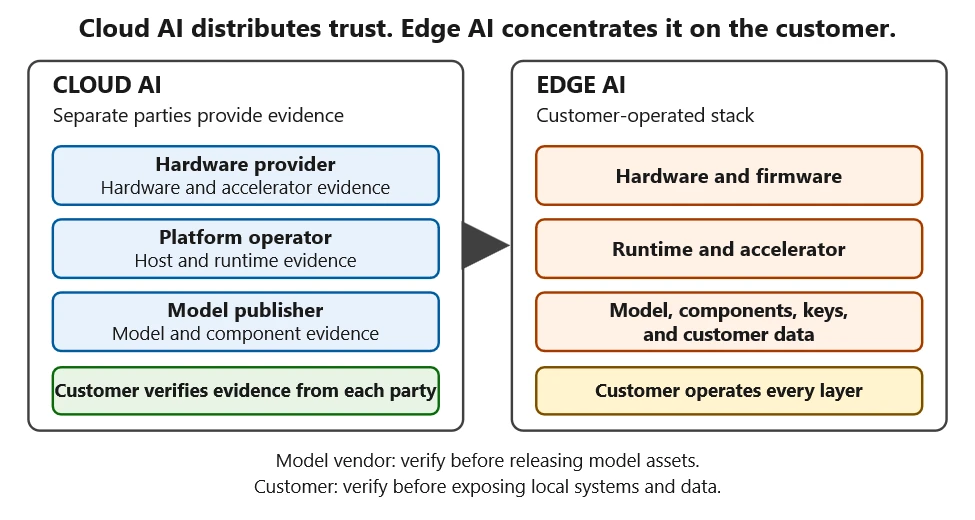
Bottom line: Organizations must ensure edge AI environments are secured with trusted, validated, and regularly updated software and AI assets to prevent data breaches and model tampering.
What's happening: Researchers from Microsoft identified 12 vulnerabilities in customer-owned edge AI environments, including CVE-2022-45377 (CVSS score 7.5), a critical vulnerability in the TensorFlow software, which could be exploited by attackers to access sensitive data and compromise AI models. The vulnerabilities were found in AI environments in the United States, United Kingdom, and Australia, and affected approximately 10% of all edge AI environments.
What to do: Security leaders should conduct regular security assessments and validate the trustworthiness of software and AI assets before deploying them to edge AI environments. They should also ensure that AI environments are regularly updated with the latest security patches and that all personnel have access to comprehensive training on AI security best practices.