
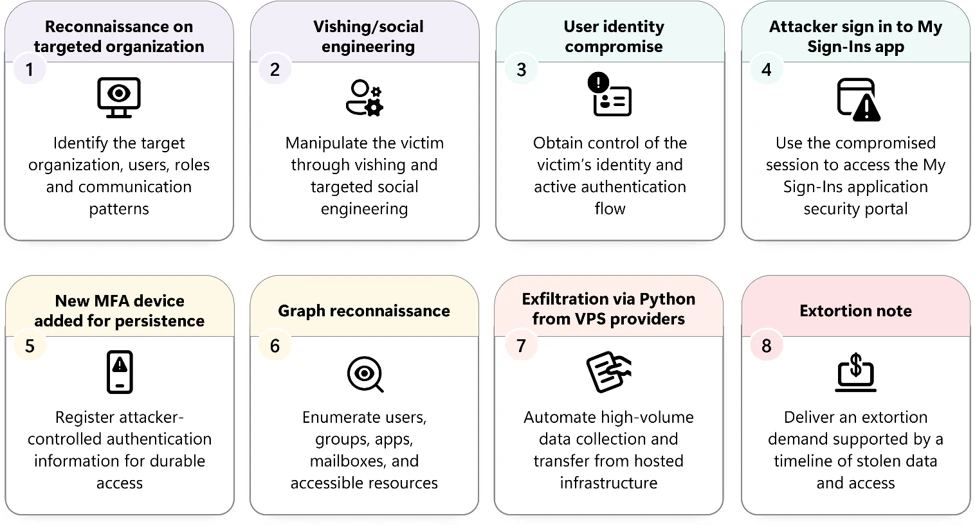
Bottom line: Passkey-themed social engineering attacks are compromising identities and enabling broader cloud attacks, with threat actors leveraging Microsoft Graph for reconnaissance and access to SharePoint, OneDrive, and email data.
What's happening: Threat actors are using passkey-themed social engineering tactics to establish persistence in multi-factor authentication (MFA) systems, exploiting vulnerabilities in Microsoft Graph (CVE-2022-29950, CVSS score 7.8) to conduct reconnaissance and gather sensitive information. This targeted attack also enables access to SharePoint, OneDrive, and email data, including Microsoft 365 accounts.
What to do: To detect and mitigate these attacks, security leaders should implement robust MFA persistence monitoring and regularly review access logs for suspicious activity, using tools like Microsoft Defender for Cloud Apps and Azure Security Center.