
Every benchmark tells a story. The most valuable ones tell us where to improve next.
For five consecutive quarters Microsoft has published email security benchmarking reports to provide greater transparency into real-world protection outcomes. The results have shown strong Microsoft Defender performance across pre-delivery and post-delivery scenarios, while revealing where threats and defenses continue to evolve.
This quarter’s benchmark examines how continuous measurement informs protection across prevention, detection, and adaptation, and how those insights are helping improve customer outcomes.
Read the latest Microsoft benchmarking data for email securityKey takeaways
- Defender again missed the fewest high-severity threats among the solutions evaluated, about 55% fewer than the next-closest secure email gateway (SEG) vendor.
- Layered security adds the most value in promotional and bulk filtering and works; gains for spam and malicious email remain comparatively modest.
Benchmarking results for SEG vendors
In the latest quarterly SEG comparison from May 2026 through July 2026, Defender missed 221 high-severity threats per 1,000 protected users, 55.4% fewer than the next-closest SEG vendor. The benchmark measures missed threats instead of the total number of malicious emails that were caught and filtered, because catch totals can reflect differences in threat volume and exposure across vendor environments. By normalizing missed threats per 1,000 users we are able to provide a more consistent side-by-side comparison.
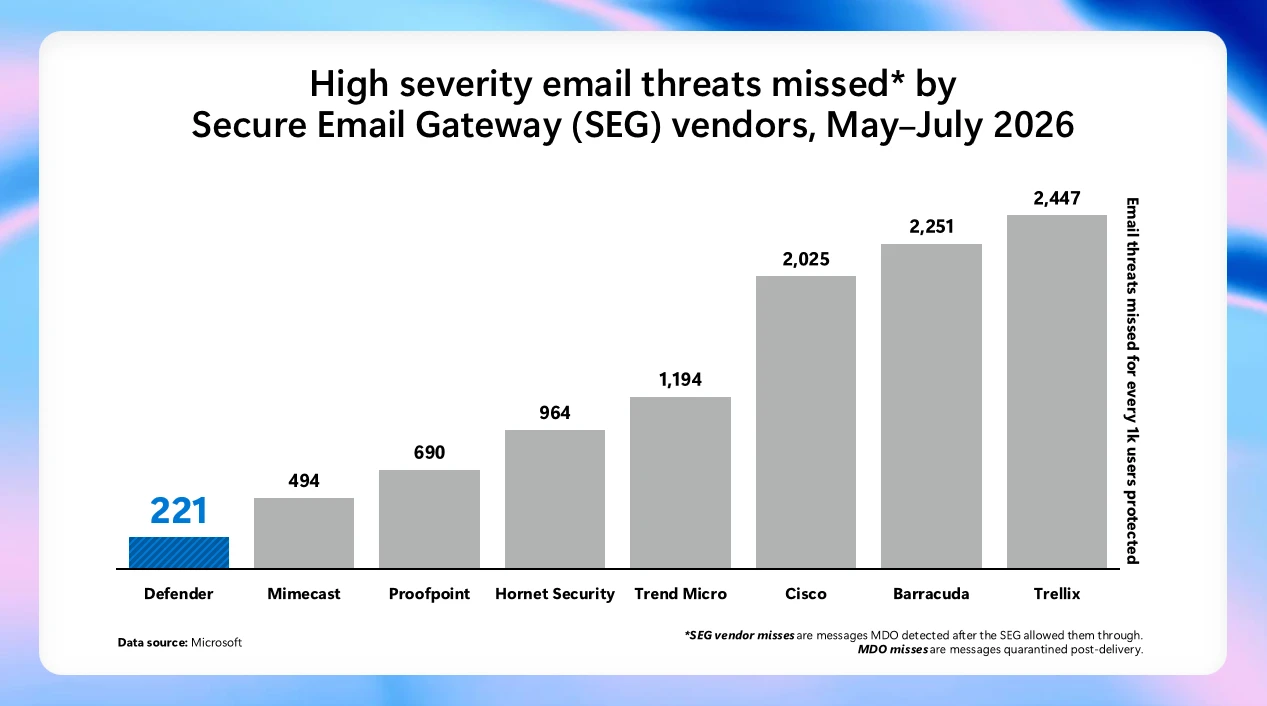 Figure 1: High-severity email threats missed by SEG vendors (May 2026 through July 2026), measured as threats missed per 1,000 users protected. Data source: Microsoft Defender.
If you’ve read our previous blogs, you’ll see that missed threats have increased across multiple reporting periods, including for Microsoft. This aligns with broader trends we’re seeing as AI makes it easier for cyberattackers to gather public information, tailor messages, and create more convincing impersonation attempts. It reinforces the need for protection that continuously adapts.
Benchmarking results for ICES vendors
Effective email detection combines pre-delivery filtering with post-delivery detection and remediation. This benchmark helps customers evaluate where each layer contributes measurable value.
Similarly to previous quarters, integrated cloud email security (ICES) solutions continue adding the most value in promotional and bulk filtering. We saw an improvement in ICES vendor malicious catch at 0.30% versus 0.13% in the last quarter and spam catch going up to 0.52% versus 0.28% compared to last quarter.
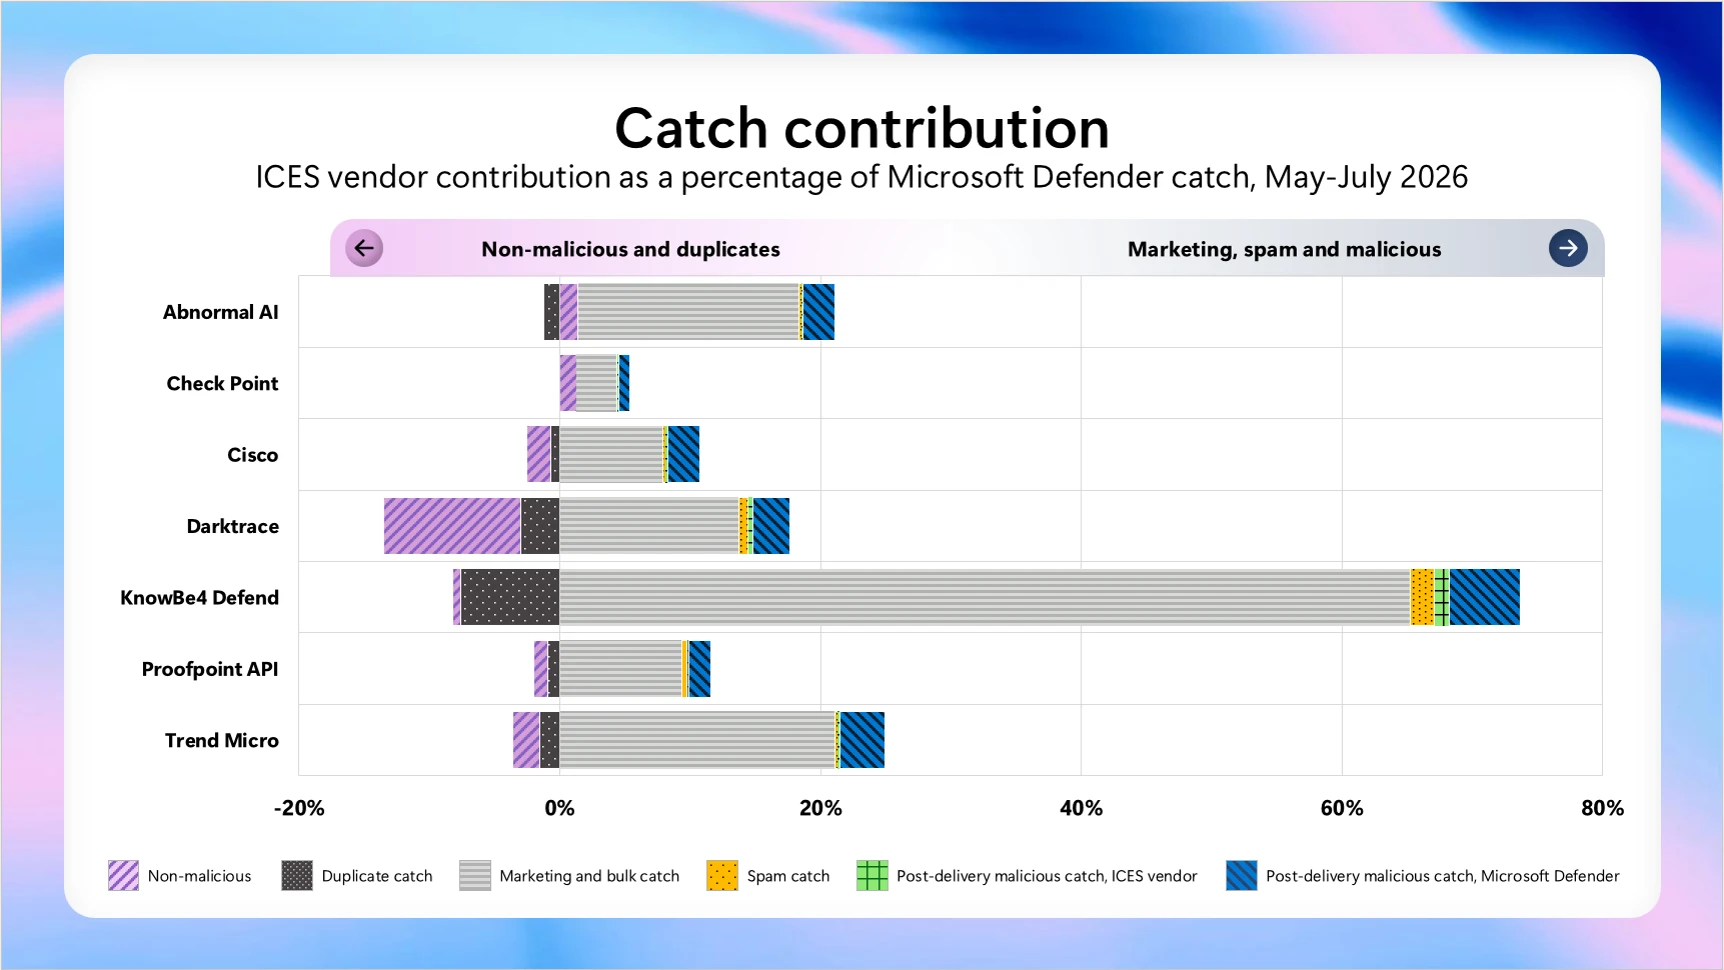 Figure 2: ICES vendor catch contribution (May 2026 through July 2026). Data source: Microsoft Defender.
Defender caught 92% of post-delivery malicious messages on average during the benchmark period, highlighting how the combination of pre-delivery and post-delivery remediation delivers strong results for customers.
At the same time it’s key to understand that Defender doesn’t treat post-delivery remediation as a point-in-time action after the email was first delivered to the inbox. Even after a message reaches the inbox, new threat intelligence can reveal risks that were not apparent at the time of delivery. Defender continuously reevaluates delivered messages and remediates threats as new indicators, campaign intelligence, and threat signals emerge.
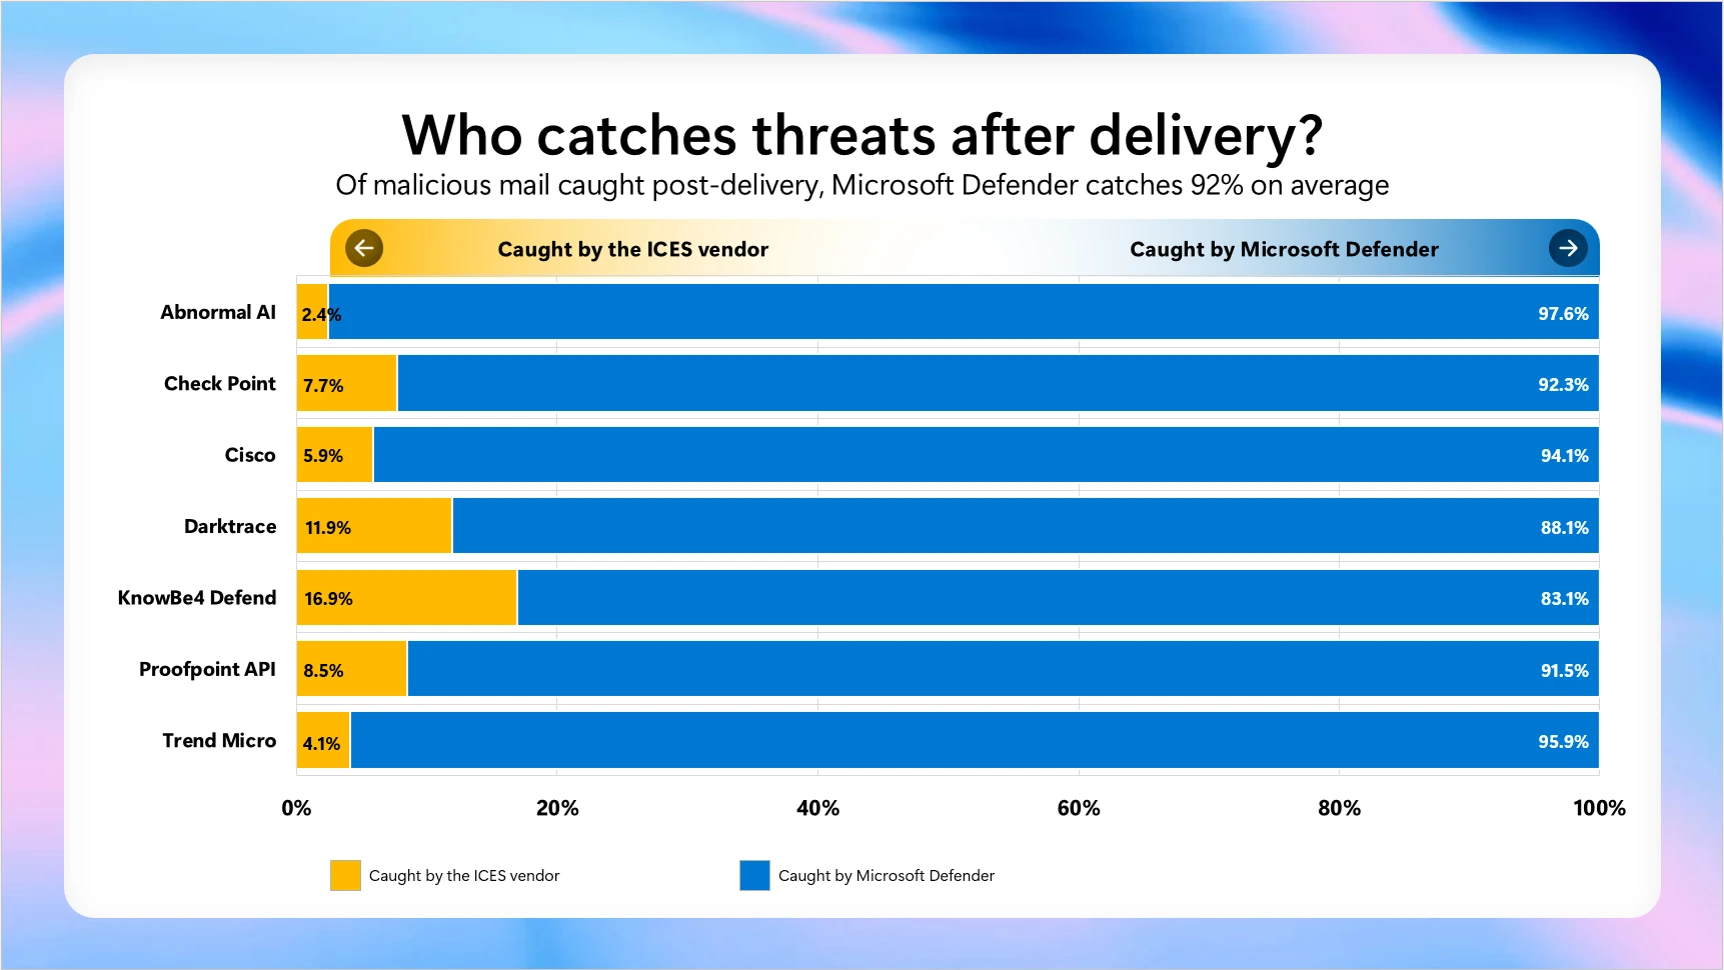 Figure 3: Post‑delivery malicious catch by Microsoft Defender (May 2026 through July 2026), shown across vendor