
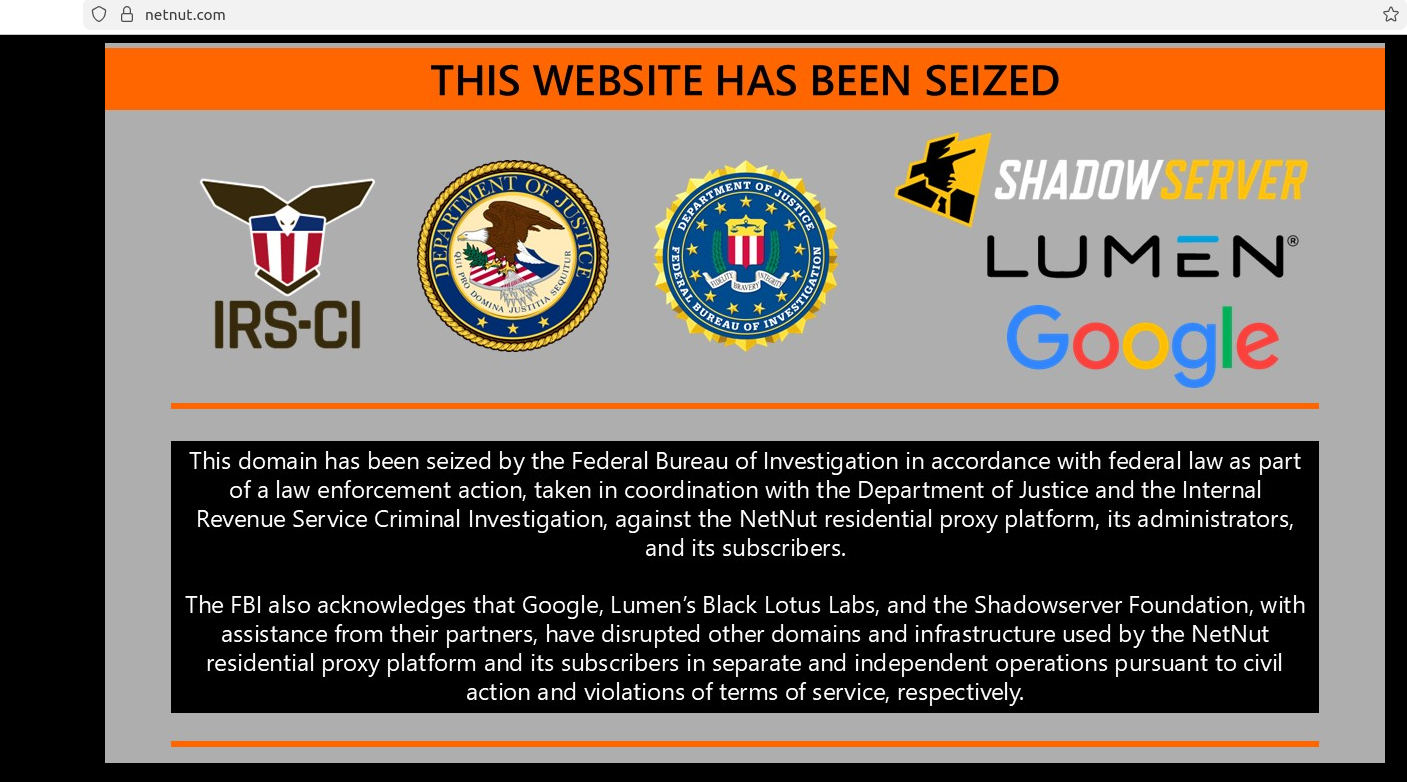
The FBI's coordinated effort with industry partners resulted in the seizure of approximately 170 domains associated with NetNut, a residential proxy service operated by Alarum Technologies. This move is aimed at disrupting the Popa Botnet, a notorious malware network that has been linked to various cyber threats, including ransomware attacks and botnet operations. The Popa Botnet is believed to be one of the largest and most destructive botnets in recent years, affecting multiple countries and impacting a wide range of industries.
The seizure of NetNut domains is a significant step in the FBI's efforts to combat cybercrime. By targeting the proxy service, the FBI is hoping to cut off the Popa Botnet's ability to communicate and conduct operations. Industry partners played a crucial role in the operation, providing critical information and assistance to help bring down the malicious network.