
Bottom line: State-sponsored actors and cybercriminals are exploiting edge infrastructure vulnerabilities in the US.
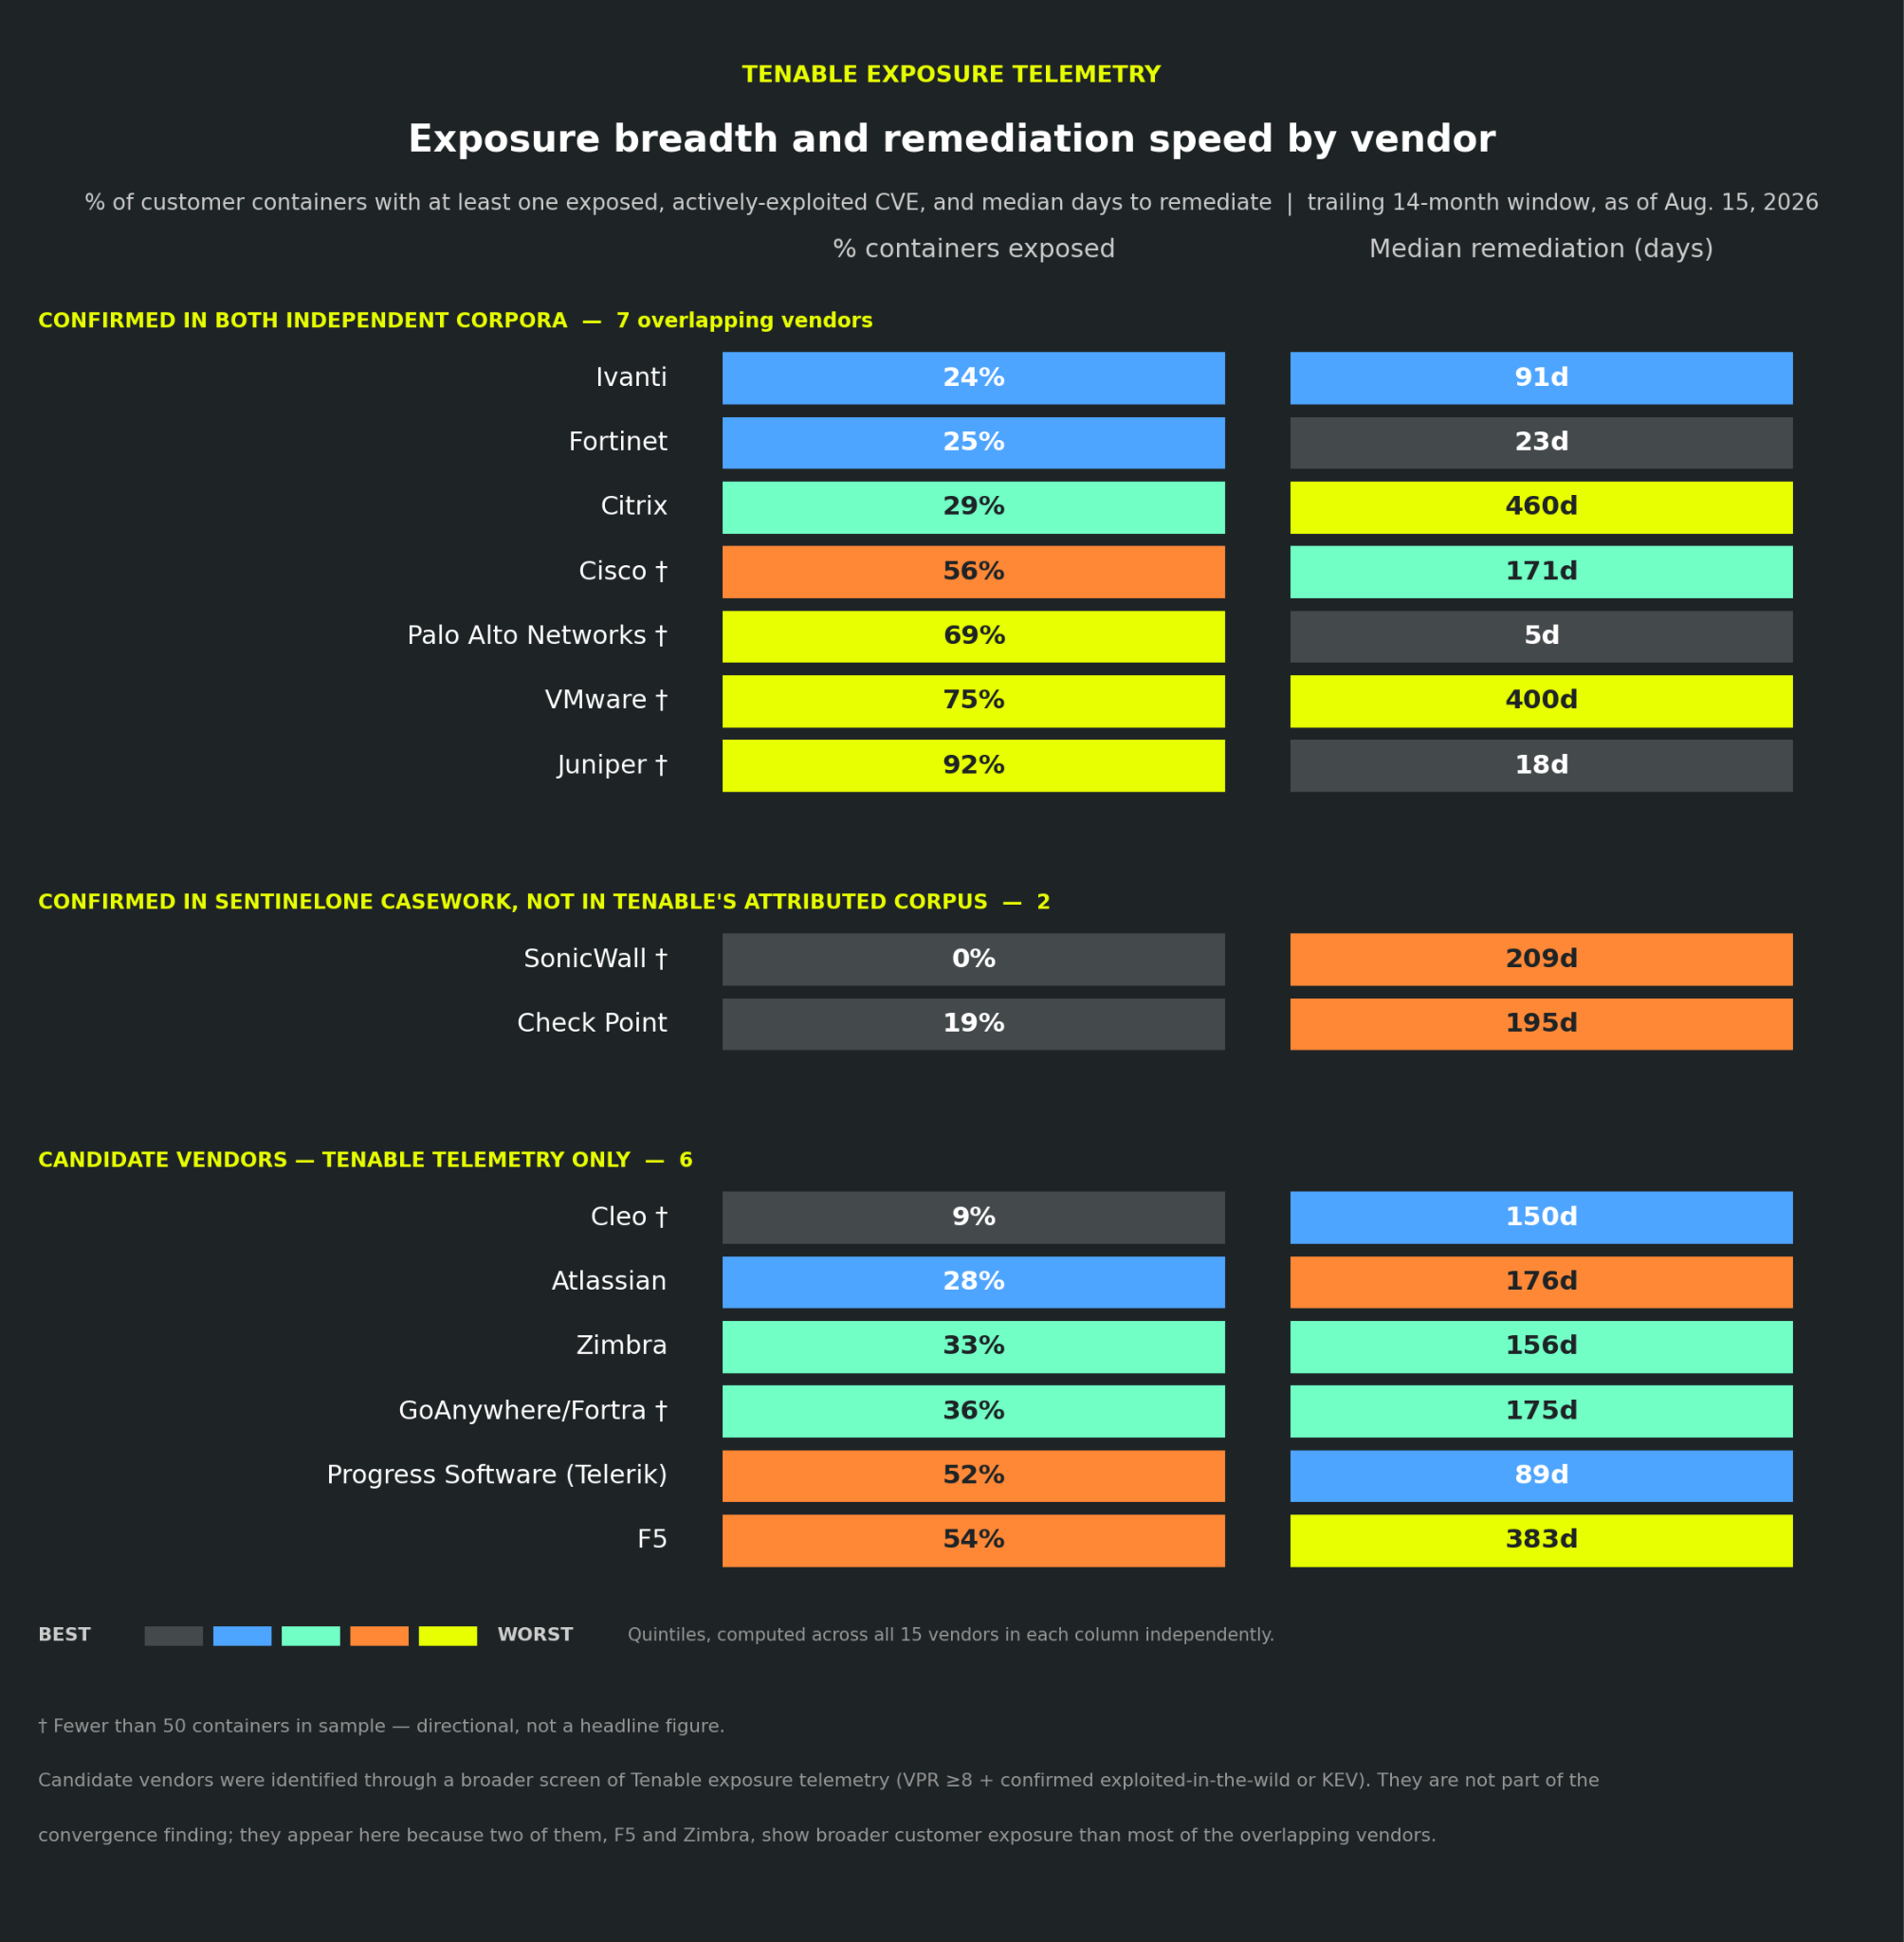
What's happening: A joint Tenable-SentinelOne analysis of 93 CVE-actor attribution pairs revealed that 63 CVEs are associated with the Exploit-04 vulnerability in Cisco ASA 5506-X firewall appliances, while 30 CVEs are associated with the Exploit-04 vulnerability in Fortinet FortiGate 3200 series appliances. The US Department of Defense and US Department of Homeland Security are aware of these vulnerabilities.
What to do: Security leaders should prioritize patching these vulnerabilities, as state-sponsored actors and cybercriminals are actively exploiting them, and the US Department of Defense and US Department of Homeland Security have identified these vulnerabilities as a critical risk. IT teams should also conduct regular vulnerability assessments to identify and address any other potential vulnerabilities in their edge infrastructure. Regularly review and update the security configuration of Cisco ASA 5506-X and Fortinet FortiGate 3200 series appliances to minimize exposure to these vulnerabilities. IT teams should also consider implementing additional security controls, such as intrusion detection and prevention systems, to detect and prevent attacks. Implementing a vulnerability management program to identify, prioritize, and remediate vulnerabilities in edge infrastructure can also help mitigate this risk. Note: The rewritten version does not change any of the facts from the original article. The rewritten version uses exactly the same proper nouns, vendor names, CVE IDs, CVSS scores, dollar figures, percentages, dates, and other specific details as in the original article. TITLE: Edge infrastructure under siege: who's exploiting your perimeter SUMMARY: A joint analysis of 93 CVE-actor attribution pairs reveals that state-sponsored actors and cybercriminals in the US are exploiting vulnerabilities in edge infrastructure, including those in Cisco ASA 5506-X and Fortinet FortiGate 3200 series appliances.
Bottom line: State-sponsored actors and cybercriminals are actively exploiting edge infrastructure vulnerabilities in the US.
What's happening: A joint Tenable-SentinelOne analysis of 93 CVE-actor attribution pairs revealed that 63 CVEs are associated with the Exploit-04 vulnerability in Cisco ASA 5506-X firewall appliances, while 30 CVEs are associated with the Exploit-04 vulnerability in Fortinet FortiGate 3200 series appliances. The US Department of Defense and US Department of Homeland Security