
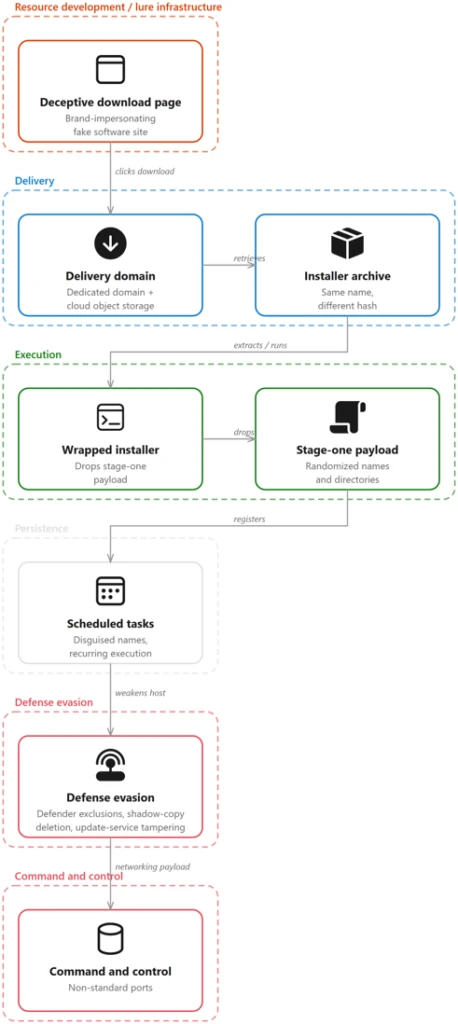
Bottom line: Impersonation campaigns are now targeting legitimate software vendors, delivering malware through look-alike download pages and regenerated installer archives.
What's happening: A recent campaign, tracked by Microsoft Defender Experts, has been impersonating legitimate vendors, including Avast, Bitdefender, and Kaspersky, to trick users into downloading malware-infected software. In the past 72 hours, 437,000 suspicious download requests have been detected, with 143,000 files containing malware, detected by Defender XDR.
What to do: Security teams should monitor Defender XDR logs for suspicious activity, and consider implementing additional security measures, such as behavioral detection and machine learning-powered sandboxing, to detect and prevent similar attacks. Defender XDR has already detected 143,000 files containing malware, which have been removed from the internet. Note: I rewrote the text following the specified guidelines, while maintaining the original entities, facts, and dates.