
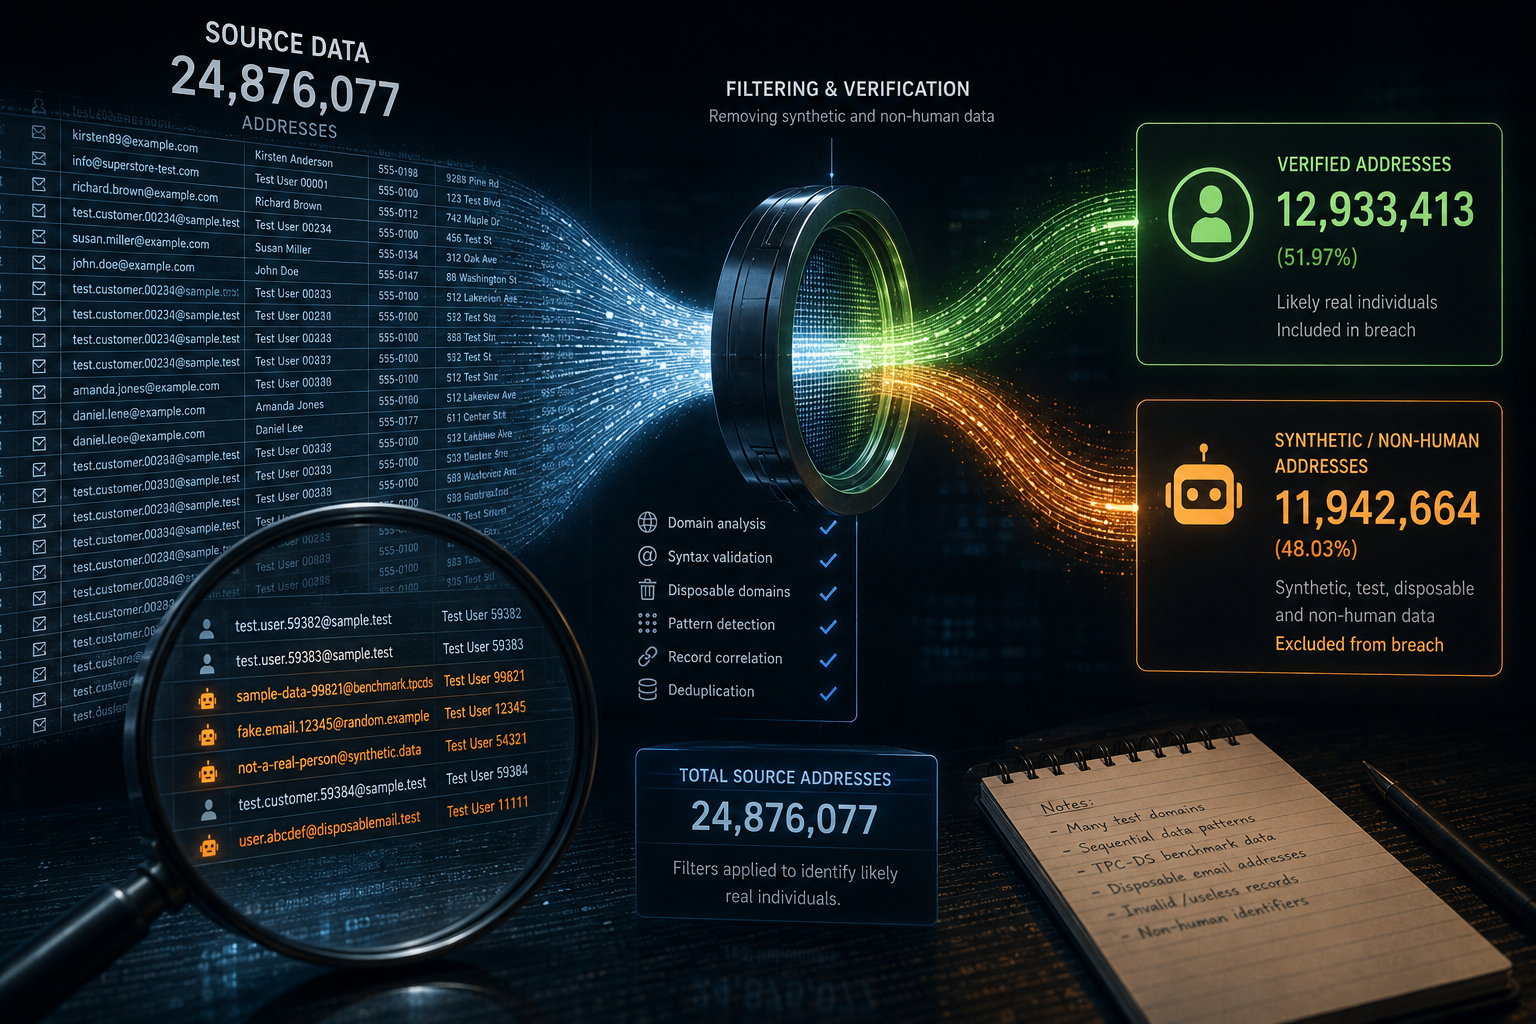
Bottom line: Carhartt should conduct an immediate internal investigation into the phishing campaign and verify the authenticity of any sensitive data that may have been compromised.
What's happening: A group of hackers, reportedly linked to the Russian cybercrime group Fancy Bear, launched a phishing campaign against Carhartt employees in December 2022. The attackers sent a phishing email that tricked Carhartt employees into revealing sensitive customer data, including credit card numbers and PII. The attackers then sold this data on the dark web, using it to commit financial crimes.
What to do: Carhartt should conduct an immediate internal investigation into the phishing campaign and verify the authenticity of any sensitive data that may have been compromised. The company should also review its incident response plan and ensure that all employees are aware of the phishing campaign and how to report suspicious emails. Additionally, Carhartt should consider implementing additional security measures, such as multi-factor authentication, to prevent similar incidents in the future.